Real estate wire fraud is a scam where criminals impersonate trusted parties to redirect money during a property transaction.
These transactions often involve large wire transfers, and time-sensitive communication between buyers, sellers, lawyers, real estate agents, title companies, notaries, and financial institutions.
Together, these factors make real estate transactions a prime target for fraud.
For high-net-worth individuals, and executives, the risks can be especially significant.
Property purchases and sales may involve large sums of money, multiple advisors, and sensitive personal or financial information. A single fraudulent email or payment can lead to substantial financial loss.
The most important rule is simple: before sending money, always verify wire instructions by phone using a trusted number you already have, not one provided in an email.
These losses show how common and damaging real estate fraud can be. In many cases, the victim believes they are sending funds to a legitimate party, only to discover that the money was redirected to a fraudulent account.
How the attack works
Attackers often begin by gaining access to an email account involved in the transaction or by impersonating one of the parties. They may silently monitor the conversation and wait for the right moment to intervene.
Once attackers understand the details of the deal, they send a convincing email with fraudulent bank details that redirect the money to the attacker. Attackers may impersonate any party involved in the transaction, such as a real estate agent, lawyer, title company representative, or even the buyer or seller themselves.
Because the attacker may know specifics like dollar amounts, property addresses, and names of people involved, the message can look legitimate, making the email extremely convincing.
How to protect yourself
The most effective protection is independent verification. Before sending any wire transfer, call the intended recipient using a trusted phone number that was provided in person, saved previously, or found through an independently verified source.
Do not rely on contact information included in an email containing wire instructions. If an attacker controls the email conversation, they may also provide a fake phone number to “confirm” the fraudulent details.
This is especially important as AI voice cloning becomes more convincing. A phone call is only useful if the number is trusted. When in doubt, use a number you already know or independently verify the number through an official website or previously established contact.
The same approach should be used for any high-value payment, account change, or request involving sensitive financial information.
Red flags to watch for
Be cautious of:
- Last-minute changes to wire instructions
- Pressure to wire immediately
- Email addresses that look slightly off, such as ‘titlecompany.co’ instead of ‘titlecompany.com’
- Request to confirm payment details only via email
- Unusual urgency, secrecy, or changes in communication style
- New bank account details that were not previously discussed
However, a well-crafted attack may not include any obvious warning signs. Rather than trying to decide whether an email “looks suspicious”, treat all wire instructions as unverified until they are confirmed by phone using a trusted number.
Before sending a wire transfer
Before sending funds, take these steps:
1. Confirm the wire instructions by phone using a known, trusted number.
2. Verify the recipient's name, bank name, account number, routing number, and payment amount.
3. Do not use phone numbers or links provided in the same email as the wire instructions.
4. Be especially cautious about last-minute changes.
5. If anything feels unusual, pause the transaction and contact your advisor, bank, or security team.
How Richter Guardian can help you
Richter Guardian can help reduce the risk of wire fraud through proactive monitoring, personal cybersecurity guidance, and expert support to secure accounts, devices, credentials, and identity-related information.
If you are unsure about a transaction, receive suspicious payment instructions, or want added protection before a high-value transfer, contact us.
Ready to stay protected from digital threats, with experienced professionals overseeing your security?
A legitimate $8.7 million settlement claims process opened August 4, 2026, for victims of a 2020 Government of Canada data breach—but its publicity gives fraudsters cover to build fake portals, send phishing schemes, create impersonations and harvest personal credentials. Expect fake eligibility checks, fake claims portals and claims administrator scams involving KPMG, CRA, and class counsel through the February 2027 deadline.
This covered people whose personal or financial information in a Government of Canada online account, including the Canada Revenue Agency portal, was accessed without authorization in 2020.
KPMG is the court appointed administrator, and eligible class members can submit claims online or by mail until February 3, 2027.
The settlement is legitimate, but the publicity around it is exactly the conditions fraudsters look for:
A national news story
A real government linked payout
A real deadline
A real administrator asking people to enter a last name and the last three digits of a Social Insurance Number on a website
That combination gives criminals a credible pretext to build convincing fake eligibility checkers and claim portals, and to harvest identity data and account credentials at scale.
Our expectation
A wave of phishing email, SMS, social media advertising, sponsored search results, and voice calls impersonating KPMG, the CRA, the Federal Court, and class counsel, beginning within days of the news coverage and continuing through the February 2027 claim deadline.
The only legitimate channels and what to watch for
A copy of a government ID uploaded to a chat window
Any payment or fee. There is no fee to file a claim
Anything arriving by unsolicited text, direct message, or phone call that pushes you toward a different address, a shortened link, or an app download should be treated as fraudulent until proven otherwise.
What the fakes will look like
The following mock ups were produced by Richter Guardian for training purposes.
These are not real messages and the addresses and links shown are illustrative only.
Share them with your household, your office staff, and anyone who manages correspondence on your behalf.
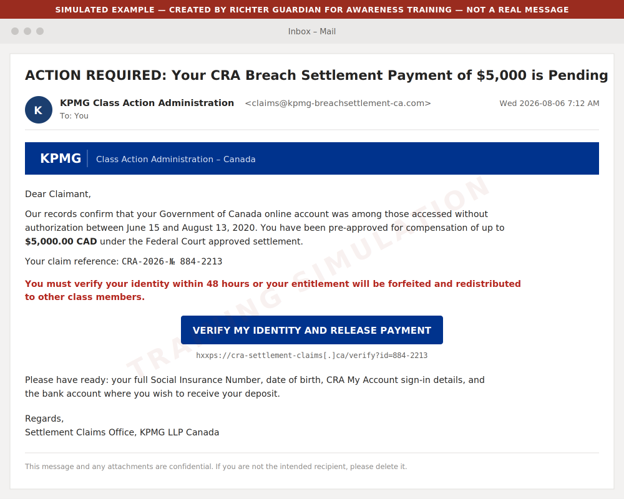
Example 1: Phishing email impersonating the claims administrator
A pre-approved dollar figure the real administrator would never quote up front
A 48 hour forfeiture threat against a deadline that is actually February 3, 2027
A request for the full SIN
CRA sign-in details
Banking information
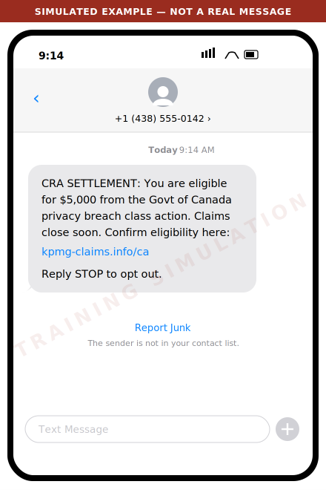
Example 2: Smishing text message
What to watch for
The administrator does not solicit claims by text message
The domain is not kpmg.ca
The amount is presented as guaranteed
Urgency is manufactured
Legitimate class action notice arrives by mail or from the administrator's own address.
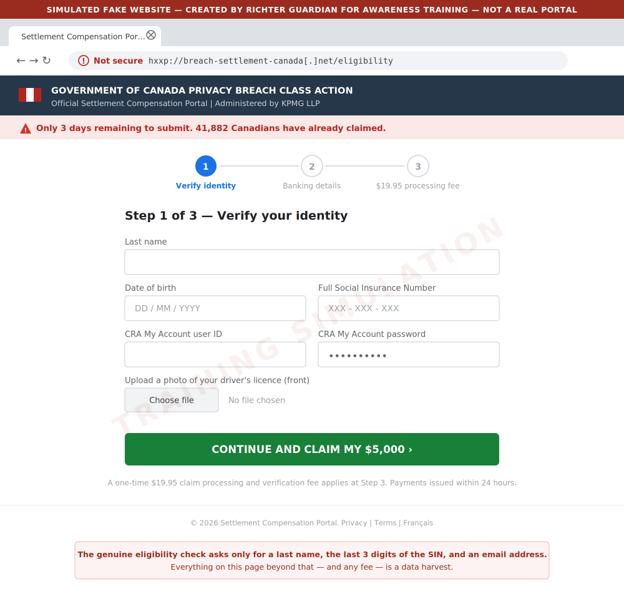
Example 3: Fake eligibility and claim portal
What to watch for
An unencrypted look-alike domain
A full SIN and CRA credentials requested where the real site asks only for a last name
Three SIN digits
An email address
An ID upload
A processing fee where the real claim is free
False scarcity counters
Criminals also buy sponsored search advertisements so these pages appear above the real one.
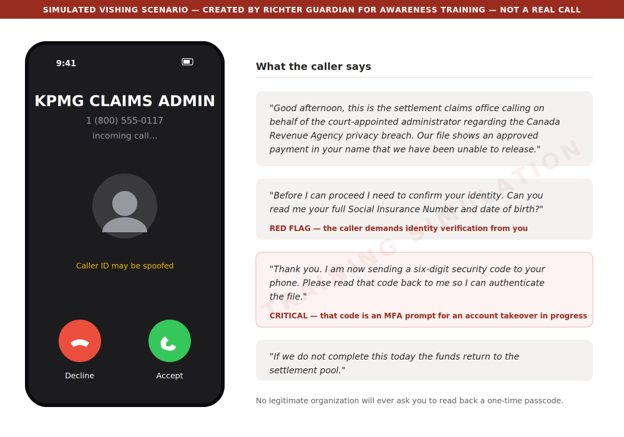
Example 4: Voice call and voicemail pre-text
What to watch for
An inbound unsolicited call
Identity verification demanded by the caller rather than by you
Above all, a request to read back a code sent to your phone. That code is a multi factor authentication (MFA) prompt for an account the caller is trying to take over at that moment. No legitimate organization will ever ask for it
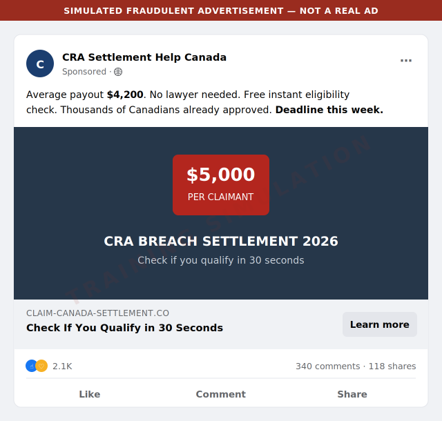
Example 5: Social media and search advertising
What to watch for
An invented average payout
A fabricated deadline
A paid placement above the genuine result
Reach the administrator by typing the address directly - https://www.breachsettlementcanada.kpmg.ca - rather than by clicking any advertisement or search result.
Red flags to brief your household and staff on
Unsolicited contact
The administrator contacts class members by mail or from its own domain. It will not cold call, text, or direct message you.
A guaranteed amount up front
Real compensation is up to $80 or up to $200 for time spent, plus up to $5,000 in documented out of pocket costs, and amounts may be reduced depending on how many claims are approved. Nobody can promise you $5,000.
Artificial urgency
The real deadline is February 3, 2027. Any message giving you 24 hours, 48 hours, or "this week" is manufacturing pressure.
Over collection of identity data
The genuine eligibility check asks for a last name, the last three digits of your SIN, and an email address. A request for the full SIN, date of birth, ID scans, or CRA credentials is a data harvest.
Any request for a fee
Filing a claim is free. A processing, verification, or expedite fee means fraud.
Any request for a code
A one time passcode read aloud, forwarded, or typed into a third party site hands over your account.
Anything ending in .info, .net, .co, .ca-claims, or a hyphenated variant of the KPMG name is not it.
Payment by unusual method
Requests to move funds, buy gift cards, or receive a payout through e-transfer to a new recipient are not part of any settlement.
What we recommend you do
For principals and family members
Type the address, never click
Reach the eligibility check only by typing https://www.breachsettlementcanada.kpmg.ca into the web browser. Do not use links from email, text, social media, or search advertisements.
Verify by calling back
If someone claims to be the administrator, hang up and contact breachsettlementcanada@kpmg.ca from the details on the official site.
Treat the SIN as a credential
Never provide a full Social Insurance Number to an inbound contact.
Check your CRA account directly
Sign in to CRA My Account by typing the address, confirm your direct deposit details and mailing address have not been changed, and enable multi factor authentication if it is not already on.
Consider a credit file alert
If you believe your information was exposed, place a fraud alert with Equifax Canada and TransUnion Canada.
For family offices and business staff
Brief your team this week
Forward or print this email to anyone who handles correspondence, banking, or tax filings on a principal's behalf.
Add a verification step
Any instruction arising from a settlement, refund, or government notice must be verified by an out of band call to a known number before any data or funds move.
Watch for lookalike domains
Ask your IT provider to monitor for newly registered domains that combine your family or firm name with settlement, claim, refund, or CRA terms.
Tune your email filtering
Quarantine newly registered sender domains and flag external mail referencing CRA settlements or class action payouts.
Report and preserve
Report suspected scams to the Canadian Anti-Fraud Centre at 1-888-495-8501 and preserve the original message headers rather than deleting them.
If you think you've already been caught
Move quickly
Change the password on any account whose credentials were entered, starting with CRA My Account and your email, and revoke active sessions.
Call the CRA
If CRA credentials were disclosed, contact the CRA immediately and ask that the account be locked and reviewed for changes to direct deposit or address.
Notify your bank
Report the exposure and ask for enhanced verification on outbound payments.
File a credit alert
Contact Equifax Canada and TransUnion Canada.
Contact Richter Guardian
Speak to your Richter Guardian team. We can help contain the incident, assess what was exposed, and coordinate monitoring.
Ready to stay protected from digital threats, with experienced professionals overseeing your security?
Real estate wire fraud is a scam where criminals impersonate trusted parties to redirect money during a property transaction. For high-net-worth individuals, and executives, the risks can be especially significant.
Read more
Introduction
Real estate wire fraud is a scam where criminals impersonate trusted parties to redirect money during a property transaction.
These transactions often involve large wire transfers, and time-sensitive communication between buyers, sellers, lawyers, real estate agents, title companies, notaries, and financial institutions.
Together, these factors make real estate transactions a prime target for fraud.
For high-net-worth individuals, and executives, the risks can be especially significant.
Property purchases and sales may involve large sums of money, multiple advisors, and sensitive personal or financial information. A single fraudulent email or payment can lead to substantial financial loss.
The most important rule is simple: before sending money, always verify wire instructions by phone using a trusted number you already have, not one provided in an email.
These losses show how common and damaging real estate fraud can be. In many cases, the victim believes they are sending funds to a legitimate party, only to discover that the money was redirected to a fraudulent account.
How the attack works
Attackers often begin by gaining access to an email account involved in the transaction or by impersonating one of the parties. They may silently monitor the conversation and wait for the right moment to intervene.
Once attackers understand the details of the deal, they send a convincing email with fraudulent bank details that redirect the money to the attacker. Attackers may impersonate any party involved in the transaction, such as a real estate agent, lawyer, title company representative, or even the buyer or seller themselves.
Because the attacker may know specifics like dollar amounts, property addresses, and names of people involved, the message can look legitimate, making the email extremely convincing.
How to protect yourself
The most effective protection is independent verification. Before sending any wire transfer, call the intended recipient using a trusted phone number that was provided in person, saved previously, or found through an independently verified source.
Do not rely on contact information included in an email containing wire instructions. If an attacker controls the email conversation, they may also provide a fake phone number to “confirm” the fraudulent details.
This is especially important as AI voice cloning becomes more convincing. A phone call is only useful if the number is trusted. When in doubt, use a number you already know or independently verify the number through an official website or previously established contact.
The same approach should be used for any high-value payment, account change, or request involving sensitive financial information.
Red flags to watch for
Be cautious of:
- Last-minute changes to wire instructions
- Pressure to wire immediately
- Email addresses that look slightly off, such as ‘titlecompany.co’ instead of ‘titlecompany.com’
- Request to confirm payment details only via email
- Unusual urgency, secrecy, or changes in communication style
- New bank account details that were not previously discussed
However, a well-crafted attack may not include any obvious warning signs. Rather than trying to decide whether an email “looks suspicious”, treat all wire instructions as unverified until they are confirmed by phone using a trusted number.
Before sending a wire transfer
Before sending funds, take these steps:
1. Confirm the wire instructions by phone using a known, trusted number.
2. Verify the recipient's name, bank name, account number, routing number, and payment amount.
3. Do not use phone numbers or links provided in the same email as the wire instructions.
4. Be especially cautious about last-minute changes.
5. If anything feels unusual, pause the transaction and contact your advisor, bank, or security team.
How Richter Guardian can help you
Richter Guardian can help reduce the risk of wire fraud through proactive monitoring, personal cybersecurity guidance, and expert support to secure accounts, devices, credentials, and identity-related information.
If you are unsure about a transaction, receive suspicious payment instructions, or want added protection before a high-value transfer, contact us.
Ready to stay protected from digital threats, with experienced professionals overseeing your security?
Protecting What You Can't Replace: A Data Backup Guide
Important family, financial, and legal information is increasingly stored across devices and online accounts, making a reliable backup plan an important part of protecting it. For many families, these types of files now exist across different devices and services, so it helps to know where those files are stored, how they can be recovered, and what their risks are.
Read more
Introduction
Important family, financial, and legal information is increasingly stored across devices and online accounts, making a reliable backup plan an important part of protecting it.
For many families, these types of files now exist across different devices and services, so it helps to know where those files are stored, how they can be recovered, and what their risks are.
For high-net-worth individuals, families, and executives, backups are especially important because the information they rely on is often highly valuable, private, and difficult to replace. A lost device, ransomware attack, cloud account issue, or hardware failure can quickly disrupt personal, financial, or business matters.
Having a reliable backup plan helps ensure important files remain accessible, protected, and recoverable when something goes wrong.
Common risks to your data
Data can be lost in several ways, including lost or stolen devices, ransomware, or everyday backup failures such as cloud service outages, file corruption, or hardware failure.
Lost or stolen devices
If a device is lost, stolen, or destroyed, any files stored only on that device may be permanently lost. The best protection is to keep a backup in another place, such as a cloud account or an external hard drive.
Ransomware
Ransomware is another serious risk. This type of attack locks your files and demands payment to restore access. An offline backup, such as an external hard drive, protects your files since attackers cannot access it.
Everyday backup failures
Backups can also fail for everyday reasons. Automatic backup settings may be turned off, an important folder missed, files become corrupted, or a cloud service may be temporarily unavailable. A helpful rule of thumb is to keep three copies of important data: one on your device, one in the cloud, and one on an external hard drive.
Cloud backup as a first layer of protection
Cloud storage saves your data online through a service such as Google Drive, Apple iCloud, or Microsoft OneDrive. You can access files from any device with an internet connection, and many cloud services can back up your files automatically.
Cloud services you may already use
Apple iCloud
Included on all Apple products (iPhone, iPad, Mac)
Can be set to automatically back up photos, videos, contacts, documents and text messages
Google Drive
Built into many Android devices and Chromebooks through a Google account
Windows and Mac users need to install Google Drive for desktop and choose which folders to sync
Microsoft OneDrive
Built into Windows 10/11 and included with Microsoft 365 subscriptions
Can be set to automatically back up your Desktop, Documents, and Pictures folders
Using cloud backup securely
Start by confirming that cloud backup is turned on for each device and the right files and folders are included.
Check that recent files are being backed up and that you have enough storage for the information you want to protect.
Since cloud backups can sync unwanted changes, including ransomware-encrypted files, cloud backup should be paired with an offline backup that is disconnected when not in use.
Using a hard drive as an offline backup
An external hard drive provides an extra layer of protection if something goes wrong with your device or cloud account.
To use an external hard drive, connect it to your computer, copy your important files, and disconnect it once the backup is complete.
For added safety, store the drive in a secure location away from your main devices. A safety deposit box or personal safe is the most secure option.
A good place to start
Identify the files that would be hardest to replace, such as legal documents, financial records, tax documents, insurance information, and family photos.
Confirm cloud backup is turned on and includes those files.
Protect cloud accounts with strong passwords and multi-factor authentication.
Copy important files to an external hard drive and disconnect when finished.
Store the hard drive somewhere safe, and separately from your main devices.
Test your backups periodically to make sure the files can be recovered.
If you’re a Richter Guardian client and have questions about securing your backup accounts, multi-factor authentication, protecting your devices from ransomware, or improving your overall device backup strategy, please contact our team.
Ready to stay protected from digital threats, with experienced professionals overseeing your security?